Customer-facing businesses depend on digital systems for everyday interactions. A client may book an appointment online, create an account, submit payment information, or communicate through a support portal. Each interaction creates a potential entry point for attackers. Business leaders therefore need to consider cybersecurity as part of customer operations, with protections covering both the systems customers see and the technology operating behind them.
Secure the Login Before Anything Else
Account credentials remain a valuable target because gaining legitimate access can allow an attacker to bypass other defenses. Multi-factor authentication can reduce that risk, particularly for employees and administrators with access to customer records.
Businesses should also limit repeated login attempts and watch for unusual authentication patterns. Hundreds of attempts against multiple accounts, for example, may indicate credential stuffing rather than customers simply forgetting passwords.
Access should remain limited after login. A customer service employee may need to view an account without having permission to download an entire customer database. Restricting privileges reduces the potential damage if an account is compromised.
Follow Customer Data Through the Business
A website form is often only the beginning of a customer’s data journey. Submitted information might move into a CRM, payment platform, scheduling application, email system, or cloud database.
Leadership should map those connections and determine what information each system receives. Data collection deserves scrutiny too. If a business asks customers for information it never uses, eliminating those fields reduces the amount of data that could eventually be exposed.
The same review should include outside integrations. A company using ClickSWITCH or another third-party platform should determine what information moves between systems, which permissions are required, and who is responsible for monitoring the connection.
Look Beyond Obvious Signs of an Attack
A successful login does not necessarily mean the correct person controls the account. Businesses should monitor what users do after authentication.
A customer account that suddenly changes its email address and payment details or downloads an unusual volume of documents deserves attention. Similar scrutiny should apply to employee accounts that begin accessing records outside their normal responsibilities.
Clear logs make these events easier to investigate. Authentication activity, administrative changes, failed access attempts, and significant account actions should be recorded for an appropriate period.
Prepare for Disruption Before Customers Notice It
Cybersecurity planning should include what happens when a system becomes unavailable. Businesses need reliable backups, but a completed backup notification is not proof that recovery will work. Periodic restoration tests can confirm whether critical information is actually recoverable.
Leaders should also establish who handles a suspected incident, how affected systems will be isolated, and how essential customer services can continue. Contact information for relevant technical, legal, insurance, and communications resources should be available before an emergency occurs.
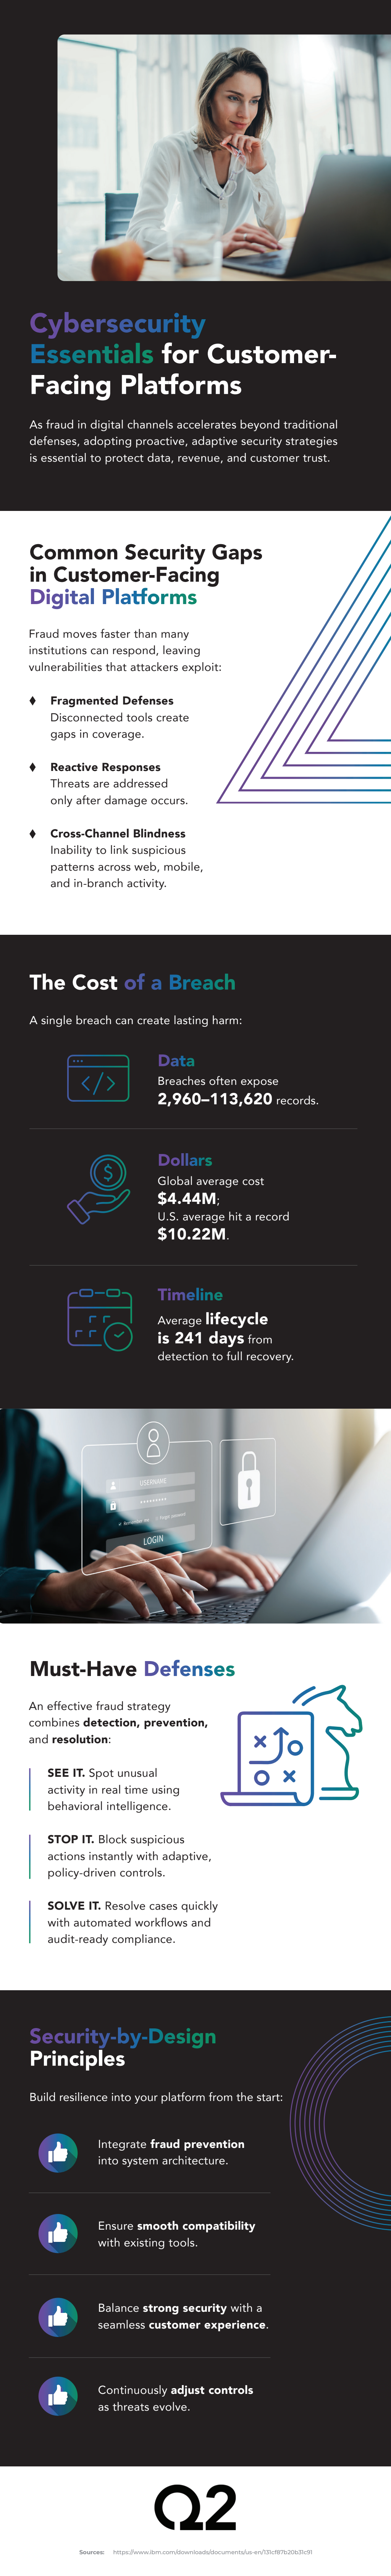
Customer-facing cybersecurity is strongest when protection follows the entire customer interaction rather than stopping at the website. Authentication, limited access, careful data collection, third-party oversight, activity monitoring, and recovery planning work together to reduce exposure. Check out the infographic below to learn more.